Agentic AI Security Needs Filtered IPO
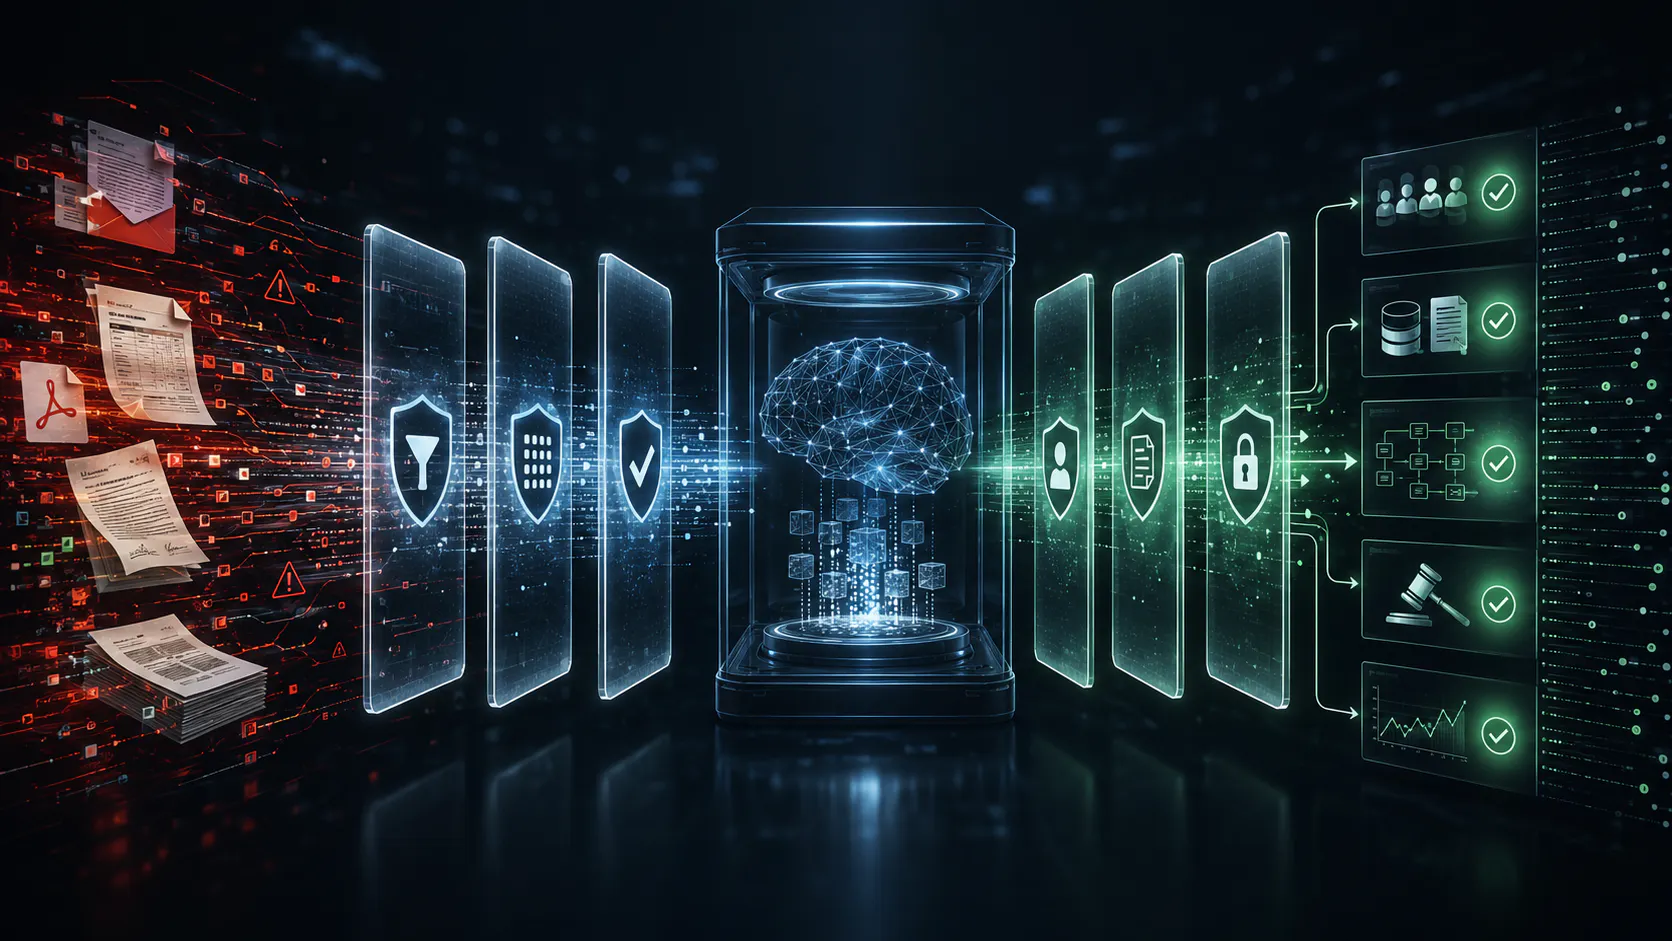
The AI era is not a post-engineering era. A boundary-first pattern for security, governance, and auditability in agentic AI workflows.
Prompt-injection attacks are not just an AI cybersecurity problem. They are a symptom of weak agentic architecture: raw inputs travel too far, agents lack clear boundaries, and reading, reasoning, tool access, and execution collapse into the same operational path.
The Real Problem Is Architectural
We treat AI like magic that makes classic IT engineering obsolete — just throw data at it and let one super-intelligent agent handle everything.
At first, I thought this was just an immaturity problem. Agentic AI is new, so the lack of reliable architectural patterns looked like an early-adoption issue that would fade with maturity. But it increasingly looks like a common practice, not a temporary mistake.
That temptation becomes dangerous when agentic systems process real documents: invoices, emails, PDFs, support tickets, purchase orders, contracts, or...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE