Agent Security & Identity (Part 2): Who Are You, Who's Your Agent, And What Should They Be Allowed?
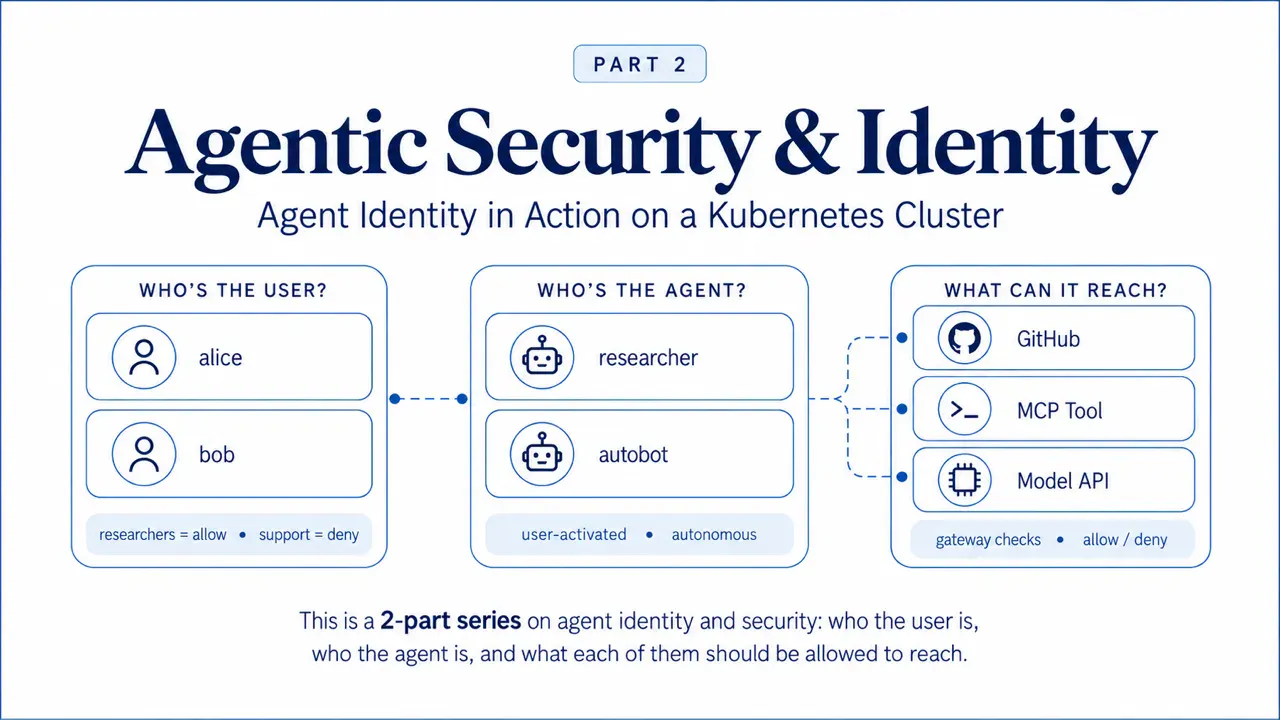
This is a 2-part series on agent identity and security: who the user is, who the agent is, and what each of them should be allowed to reach. Part 2 runs the design end to end on a cluster, with two users, two agents, a tool, a model and a third-party service.
In Part 1, I designed how agent identity can work on a platform where agent-delegation is enabled, and how we decide (+ enforce) what they and their users are allowed to reach. In this second and final part I deploy that design on a cluster and check whether it actually holds up.
In this Part 2 blog post, I go through a hands-on use-case with 2 users of the same agent platform at the same company: Alice is in the researchers group and Bob is in the support group. Throughout this I will show the good, the...
Copyright of this story solely belongs to hackernoon.com. To see the full text click HERE