2,539 secrets in 1,994 public repos: How an AI coding agent’s ‘don’t ask again’ button exposed enterprise credentials
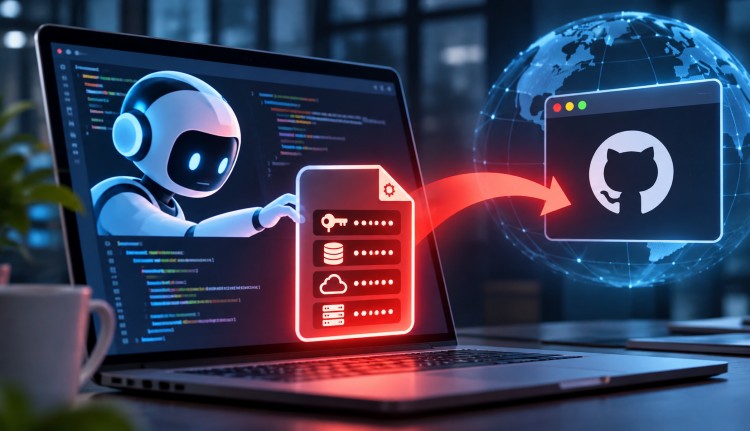
The usual story of a credential leak involves an attacker, a phishing email or a compromised server. This one involves a developer clicking “Yes, and don’t ask again.”
Application security company Apiiro has published research identifying 2,539 real secrets across 1,994 public GitHub repositories. They include database passwords, cloud access keys, API tokens and SSH credentials. The investigation found 63 organisations with exposed credentials, from startups and software agencies to established technology vendors. Some of the exposed material included production database passwords, cloud administration keys and credentials tied to medical-records applications. Some credentials had been publicly accessible for months, and a few for more than a year.
The research matters because of where the leaks originate. Developers increasingly rely on tools such as Claude Code, GitHub Copilot and Cursor to write code, troubleshoot applications, run commands and interact with enterprise systems. Apiiro’s findings suggest that the routine mechanics of those...
Copyright of this story solely belongs to www.expresscomputer.in. To see the full text click HERE