100+ Ukrainian Websites Hacked to Install Lunex Stealer with ClickFix Lure
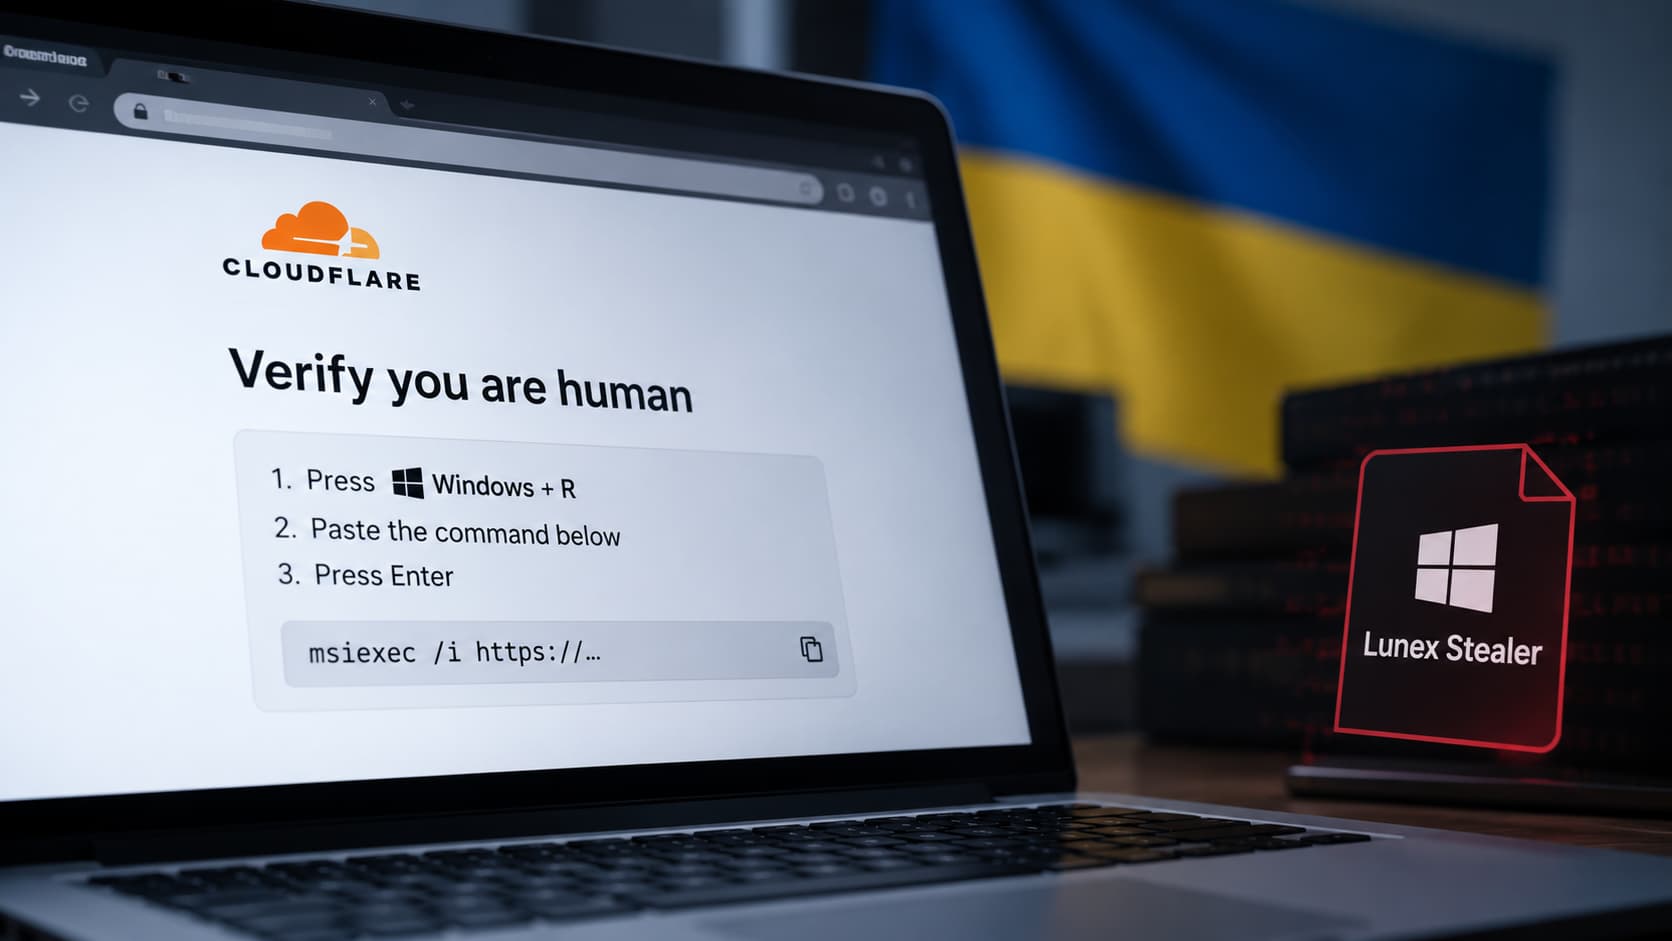
More than 100 legitimate websites in Ukraine were compromised and modified to display fake Cloudflare verification pages that installed information-stealing (infostealer) malware on Windows computers.
Ukraine’s Computer Emergency Response Team, CERT-UA, identified the campaign in September 2026 and tracks its unidentified operators as UAC-0277. The affected sites included an online shop and a website offering colouring pages for children, showing that visitors could encounter the malicious prompt while using ordinary websites.
CERT-UA’s advisory has not disclosed how the websites were compromised, how many computers were infected or whether the campaign remains active.
Fake Verification Installs Malware
The campaign began with attackers adding malicious JavaScript to the compromised websites. When someone visited an affected page, the injected code displayed a fake Cloudflare verification screen claiming that the visitor needed to prove they were human.
The instructions asked the user to open the Windows Run dialog, Command Prompt or PowerShell and execute...
Copyright of this story solely belongs to hackread.com. To see the full text click HERE